CVE-2026-103663: Ollama Path Traversal Vulnerability and RCE Risk Explained
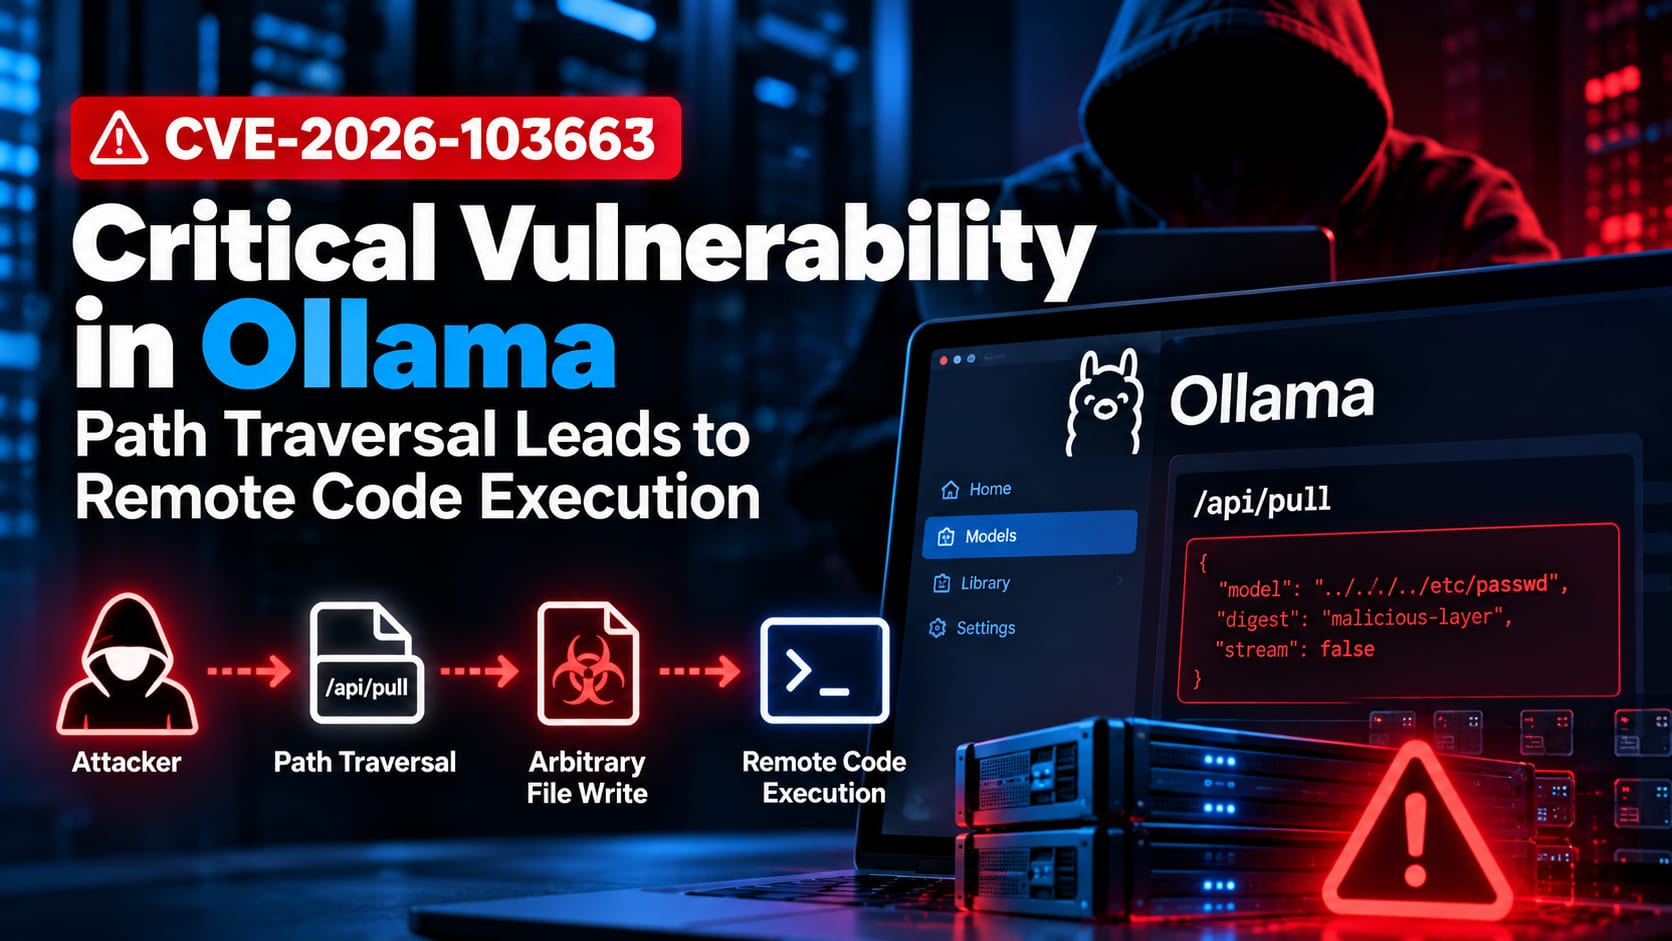
Ollama is vulnerable to path traversal in the `/api/pull` endpoint due to insufficient validation of layer digests by the `digestToPath` function.
Key takeaways
- CVE-2026-103663 has CVSS 4.0 9.4 (CRITICAL).
- It is not in the CISA Known Exploited Vulnerabilities catalogue at the time of writing.
- Apply the vendor fix or mitigation as soon as possible.
On this page
Summary
Ollama is vulnerable to path traversal in the `/api/pull` endpoint due to insufficient validation of layer digests by the `digestToPath` function. An unauthenticated remote attacker can specify a path traversal sequence as a layer digest, causing a malicious binary to be written outside the model store.
Critically if the server process has write access to `/usr/lib/ollama` (the default in most Ollama Docker images), an attacker can write the malicious file to that directory. On the next server restart, the file is loaded and executed, resulting in remote code execution as root.
This issue was fixed in version 0.35.0.
At a glance
Item | Value |
|---|---|
CVE | CVE-2026-103663 |
CVSS 4.0 | 9.4 (CRITICAL) |
Vulnerable versions | From 0.34.2 to 0.35.0 |
Weakness | CWE-23, CWE-913 |
Known exploited (CISA KEV) | Not listed |
NVD status | Awaiting Analysis |
Published | 2026-10-08 |
Last modified | 2026-10-08 |
What to do
Check the vendor advisory for fixed versions and mitigations.
Prioritise by exposure: internet-facing and unauthenticated attack paths first.
Analysis
Questions and answers
Is CVE-2026-103663 being actively exploited?
CVE-2026-103663 is not listed in the CISA Known Exploited Vulnerabilities catalogue at the time of writing.
How severe is CVE-2026-103663?
NVD rates it 9.4 (CRITICAL) under CVSS 4.0
What should I do about CVE-2026-103663?
Apply the vendor fix or mitigation, prioritising systems that are reachable from the internet.
Discussion