CVE-2026-109390: Critical AnyDesk Linux RCE - What It Is and How to Respond
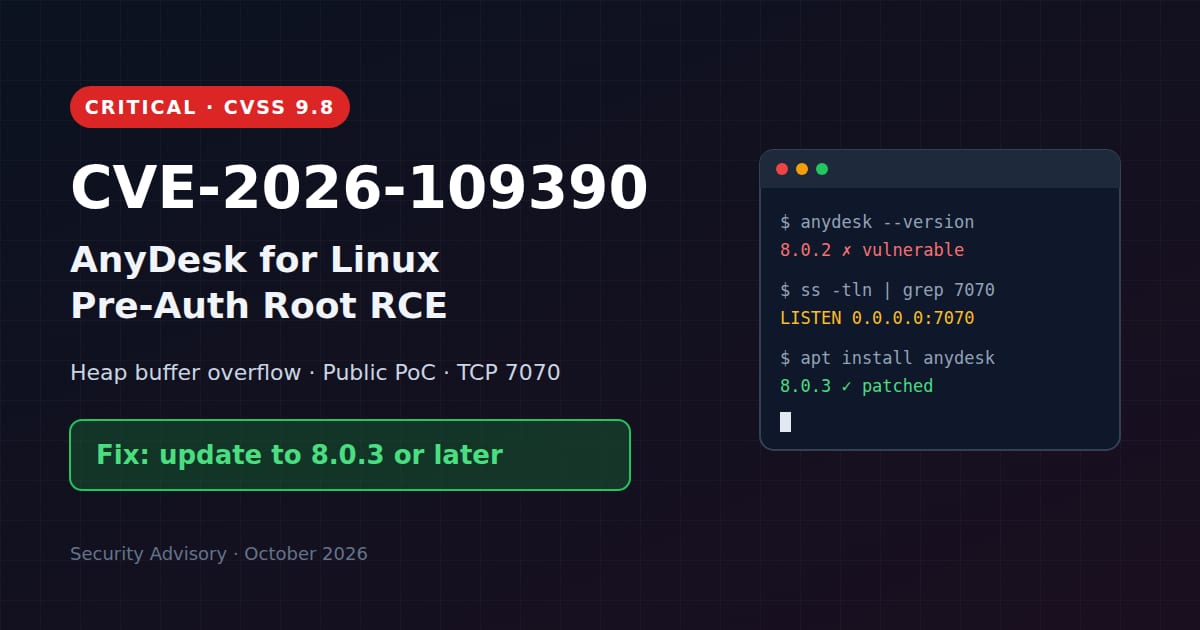
CVE-2026-109390 is a critical (CVSS 9.8) flaw in AnyDesk for Linux 8.0.0–8.0.2 that lets unauthenticated attackers run code as root. Public exploit code is available. Learn which versions are affected, how to patch to 8.0.3, and how to detect signs of compromise.
4 min read